SlideServe
Menu
Préférences
© SlideServe · v2026

Enhancing Internet Accountability with Self-Certifying Addressing Schemes

brandon-hopper avatar
1 diapositives · 169 Views · Nov 03, 2014

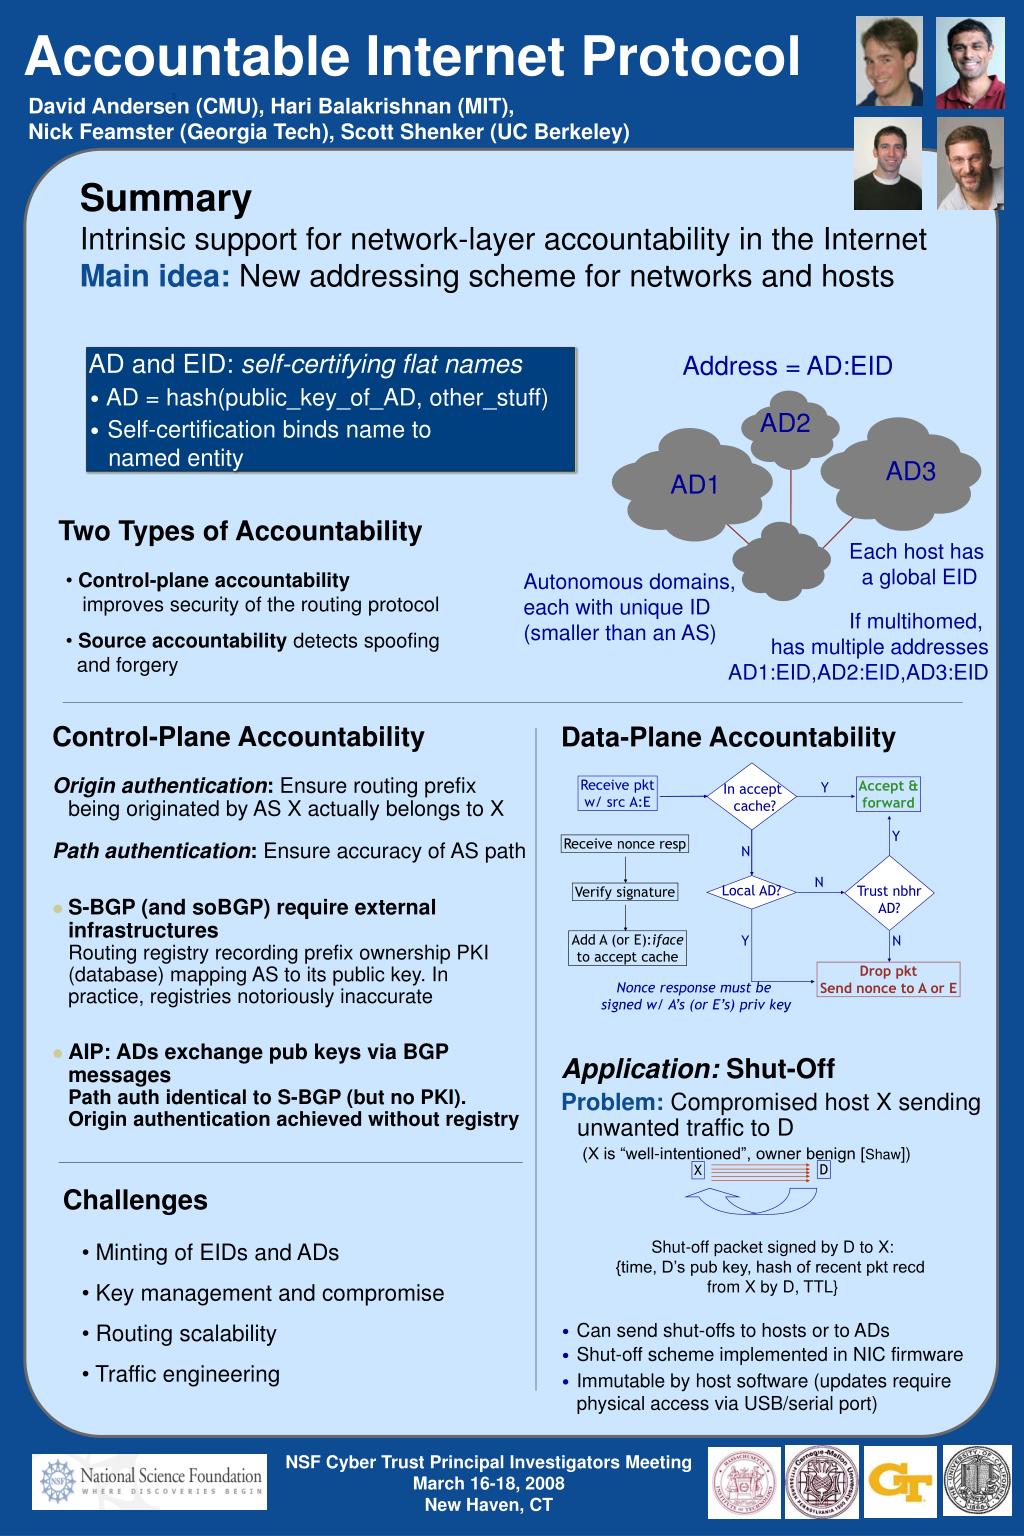
This paper presents a novel approach to network-layer accountability in the Internet through a self-certifying addressing scheme. By introducing Addressable Data (AD) and Endpoint Identity (EID) as flat, self-certifying names tied to public keys, the scheme enhances security against spoofing and forgery. Each host is assigned a unique EID, enabling improved accountability at both control and data planes. We explore the implications for routing authenticity, particularly origin and path validation, while addressing challenges in key management and routing scalability to safeguard against unwanted traffic.
Enhancing Internet Accountability with Self-Certifying Addressing Schemes - slide 1
01 / 1Enhancing Internet Accountability with Self-Certifying Addressing Schemes
1 / 17

Télécharger la présentation

Enhancing Internet Accountability with Self-Certifying Addressing Schemes
Une image / un lien ci-dessous est fourni (tel quel) pour télécharger la présentation

Politique de téléchargement : le contenu du site vous est fourni TEL QUEL pour votre information et votre usage personnel ; il ne peut être vendu, concédé sous licence ni partagé sur d’autres sites sans l’accord de son auteur.Le contenu vous est fourni TEL QUEL, pour votre information et votre usage personnel uniquement. Téléchargez la présentation en cliquant sur ce lien. Lors du téléchargement, si vous ne parvenez pas à télécharger une présentation, l’éditeur a peut-être supprimé le fichier de son serveur.Pendant le téléchargement, si vous ne parvenez pas à obtenir une présentation, le fichier a peut-être été supprimé par l’éditeur.

F I N

Plus de contenu associé

Transcription de la présentation
  1. Receive nonce resp Accountable Internet Protocol N Accept &forward Y In accept cache? N Add A (or E):ifaceto accept cache Trust nbhrAD? Verify signature Local AD? Y Receive pktw/ srcA:E Y N Drop pktSend nonce to A or E Nonce response must be signed w/ A’s (or E’s) priv key David Andersen (CMU), Hari Balakrishnan (MIT),Nick Feamster (Georgia Tech), Scott Shenker (UC Berkeley) • SummaryIntrinsic support for network-layer accountability in the InternetMain idea: New addressing scheme for networks and hosts • AD and EID: self-certifying flat names • AD = hash(public_key_of_AD, other_stuff) • Self-certification binds name to named entity Address = AD:EID AD2 AD3 AD1 Two Types of Accountability Each host has a global EID • Control-plane accountability improves security of the routing protocol • Source accountability detects spoofing and forgery Autonomous domains,each with unique ID(smaller than an AS) If multihomed, has multiple addressesAD1:EID,AD2:EID,AD3:EID Control-Plane Accountability Data-Plane Accountability • Origin authentication: Ensure routing prefix being originated by AS X actually belongs to X • Path authentication: Ensure accuracy of AS path • S-BGP (and soBGP) require external infrastructuresRouting registry recording prefix ownership PKI (database) mapping AS to its public key. In practice, registries notoriously inaccurate • AIP: ADs exchange pub keys via BGP messagesPath auth identical to S-BGP (but no PKI). Origin authentication achieved without registry Application: Shut-Off • Problem:Compromised host X sending unwanted traffic to D • (X is “well-intentioned”, owner benign [Shaw]) D X Challenges • Minting of EIDs and ADs • Key management and compromise • Routing scalability • Traffic engineering Shut-off packet signed by D to X:{time, D’s pub key, hash of recent pkt recd from X by D, TTL} • Can send shut-offs to hosts or to ADs • Shut-off scheme implemented in NIC firmware • Immutable by host software (updates require physical access via USB/serial port)